
STAIRs – Observations from the front line
What does STAIRs implementation really look like in practice? Drawing on assessments across multiple housing providers, this blog shares front-line insights, common challenges, and what the sector is getting right and wrong on transparency and accessibility.
Northern Max Award Winner 🏆 | GRC Hub Recognised for Growth & Investment Readiness
GRC Hub has been selected as a Northern Max award winner from a highly competitive cohort of ambitious Northern businesses, recognising excellence in strategy, growth and investment readiness.
Data Protection Audits in 2026: Modern vs Traditional Approaches (What Your Business Needs to Know)
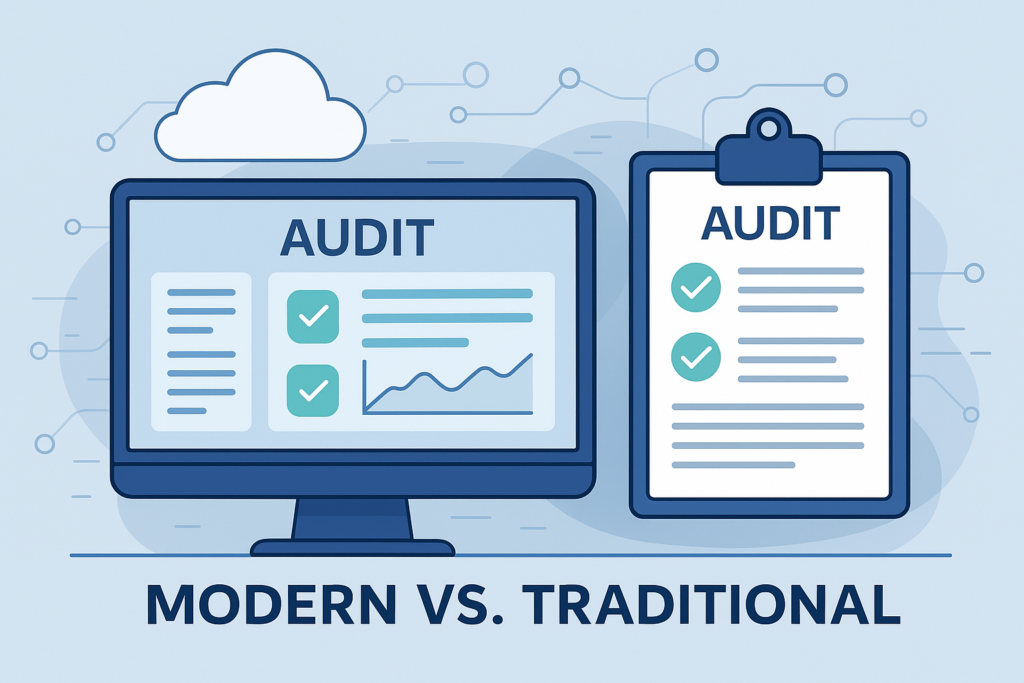
Data protection has changed dramatically in the cloud era. Traditional audits no longer reflect how modern organisations. Learn the differences between traditional and modern data protection audits, how to choose the right approach, and why continuous assurance is now essential.
PCI DSS Compliance Guide 2026: Requirements, SAQs, Merchant Levels and Breach Response
A clear and practical overview of PCI DSS v4.0.1, this guide explains what brings organisations into scope, the differences between merchants and service providers, the 12 core requirements, SAQs, payment channels, breach response and the role of acquiring banks. Ideal for retailers and social housing providers navigating modern payment security.
How Multi Site and Hybrid Organisations Can Stay Compliant with UK GDPR in 2026
Multi site and hybrid organisations face added complexity when meeting UK GDPR requirements. This guide explains how to manage governance, DSARs, data mapping, training and incident response across distributed teams, supported by the latest regulatory developments for 2026. Includes practical steps and links to GRC Hub services.
DSAR Surge 2026: How Affected Is Your Sector?
Subject Access Requests are rising across UK sectors, driven by growing complexity, resource pressure and tactical use of SARs in disputes. With proposed reforms emphasising “reasonable and proportionate” searches and greater scrutiny of SAR handling, organisations must strengthen processes to stay compliant as expectations evolve.
Data Privacy Week 2026: Practical Privacy Trends for UK Organisations
Data Privacy Week 2026 is less about awareness and more about operational reality. We explore DSAR trends, AI governance uncertainty, proportionality under the DUAA, and what organisations are actually dealing with day to day.
Data Subject Access Requests (DSARs): How to Handle Them Effectively and Stay Compliant in 2026
Data Subject Access Requests (DSARs) are a growing compliance challenge under UK GDPR. Mishandling them can lead to ICO complaints, reputational damage, and hefty fines. This guide explains why SARs are high-risk, practical steps to manage them effectively, how to handle third-party requests, and when outsourcing makes sense. Learn how to stay compliant in 2026 with clear processes, smart technology, and defensible documentation.
Third-Party Risk Management in 2025: UK Compliance, DORA, GDPR & ISO Best Practices
Learn how to manage third-party cyber risk effectively in 2025. Explore UK GDPR, ISO 27001, PCI DSS, and DORA requirements, plus insurer expectations for continuous monitoring and vendor assurance.
GRC – What we expect from 2026
Learn how to manage third-party cyber risk effectively in 2025. Explore UK GDPR, ISO 27001, PCI DSS, and DORA requirements, plus insurer expectations for continuous monitoring and vendor assurance.